
Find it, understand it, contain it, prove it.
Shadow AI is a loop, not a feature, so Sargha runs all six stages on one set of evidence.
1. Discover
Find AI on machines, cloud accounts, phones, SaaS, gateways and code. A sensor where one can run, read-only connectors everywhere else. Secrets are masked before anything leaves.
2. Understand
Turn findings into who can reach what: a graph from device to agent to tool server to key to cloud data, with every link backed by evidence. Agents and keys get owners and review dates.
3. Respond
A score you can reproduce, sharpened by live threat news matched to what you actually run. Every rating shows its reasons.
4. Test
A trust check on every AI library, tool server and skill. Safe tests of your own agents, their attack paths and chains. A pre-merge check for AI secrets and risky dependencies. A recorded engineer sign-off for AI-written code.
5. Watch
Rebuild what an AI system did, step by step. Each step is chained and signed, so an edit is found. Live response actions are planned.
6. Govern
A register of AI systems, EU AI Act tier and owner, a scored risk register, an approved-AI list and signed evidence. The tier is an accountable human decision, not an automated legal ruling.
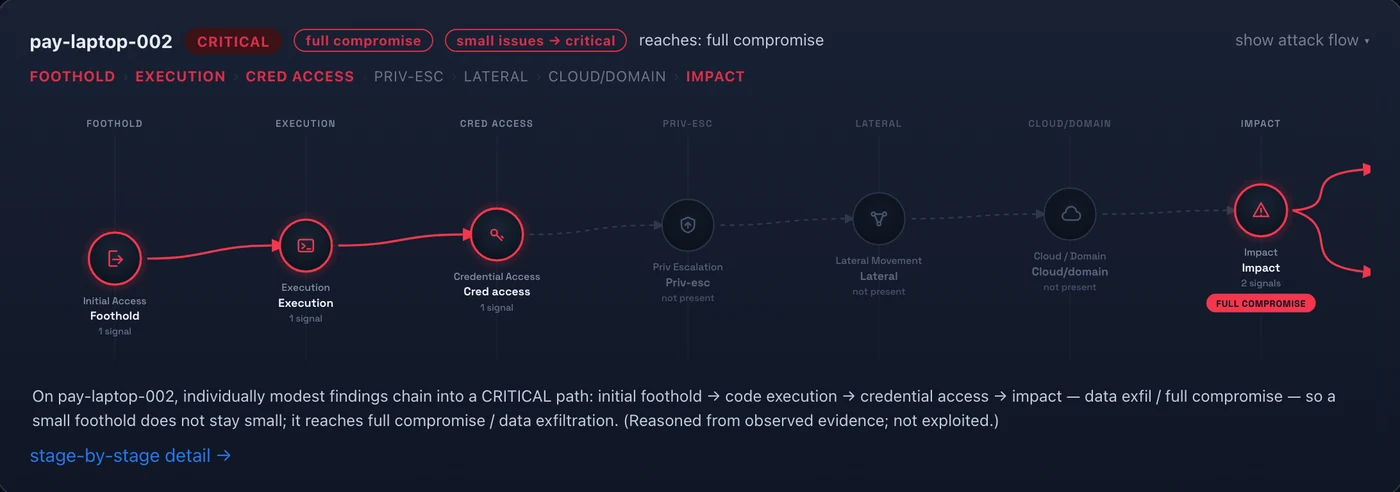
Small findings that add up to one path
For every machine with open risks, Sargha lines up the observed evidence the way an attacker would use it, from first foothold to final impact.
Step by step.
Start with discovery
The free assessment runs the first stage on up to 25 endpoints.
Connect what a sensor cannot reach
Add read-only connectors for cloud, SaaS, identity and gateways.
Extend stage by stage
Respond, test, watch and govern on the same evidence as you are ready.
Common questions.
Is it one product?
Does it block anything by default?
What does the free assessment give me?
- Nothing to start. The free assessment runs the first stage on up to 25 endpoints.
- A read-only account for each cloud or service you want connected later.
Collection, scoring and data-handling detail is in the technical pack, shared with your team under NDA.
Request the demo and technical packSee the AI on your fleet in about a week.
Run the sensor across your estate and receive an AI risk report and an AI Bill of Materials. The assessment is free and carries no commitment.